Governance Layer
SPHINX
Protect what must remain protected.
Policy, permission, and consent gates evaluate every request before protected knowledge reaches generation.
BE ALL PREMIUM VENDING
THE HOUSE IS OPENINGHOUSE NO. 001 · EST. MMXXVI
LUXURY INNOVATION EXCLUSIVITY
SCROLL TO DISCOVER
THE HOUSE OF INTELLIGENCE · CONCEPT 001
One premium destination. Distinct products, distinct licenses, and distinct proof—presented with a shared standard of discretion, precision, and permanence.
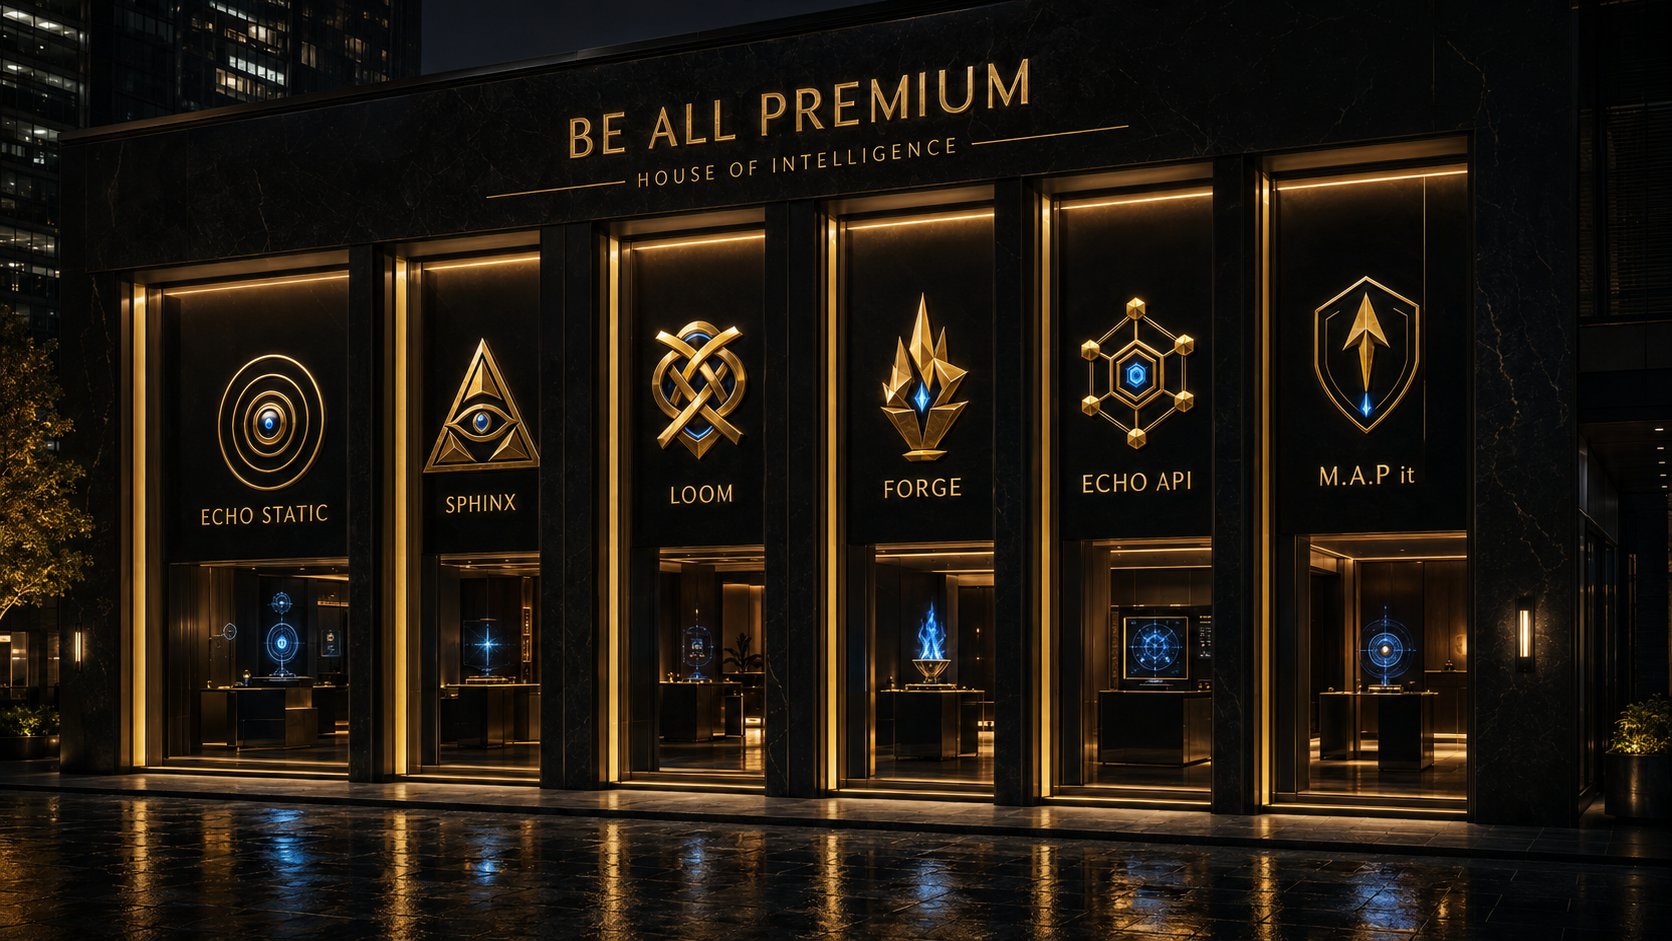 ARCHITECTURAL CONCEPT · NOT AN OPERATING LOCATION
ONE HOUSE A unified premium environment without merging product identities.
SEPARATE OFFERS Every product carries its own scope, pricing, evidence, and license.
BUILT TO EXPAND Digital licensing and pilots lead; the physical showroom is a future chapter.
This image is a design visualization, not a photograph of a completed storefront. Current product status and availability are stated individually in the catalog below.
ZEFIR-ZERO × VERITAS-BLACK X™
Step into the next evolution of digital sovereignty with ZEFIR-ZERO and Veritas-Black X—the world’s first autonomous, zero-residue security architecture engineered for high-velocity enterprise infrastructure. Powered by SIMD zero-copy ingestion, dual-channel cloud arbitration, and self-wiping cryptographic enclaves, our engine neutralizes adversarial injection and side-channel threats before they ever touch your core. When absolute data isolation is the only option, ZEFIR-ZERO doesn't just defend your perimeter—it obliterates the attack surface entirely, ensuring your operations remain untouchable, verifiable, and lightning-fast.
PRIVATE COLLECTION · 2026
A focused commercial collection spanning proprietary software, resilient OKAI fleet mobility, and private physical editions.
ECHO STATIC / BPV-E01
Where memory meets stone. Proprietary enterprise intelligence built around governance, evidence, consent, and defensible provenance.
EXPLORE THE ECHO STACK ↗PROPRIETARY SOFTWARE · COMMERCIAL LICENSING
ECHO is sold as a proprietary B2B solution—not open source. Clients license the governed outcome while the protected generation engine stays behind the ECHO API boundary.
Governance Layer
Protect what must remain protected.
Policy, permission, and consent gates evaluate every request before protected knowledge reaches generation.
Provenance Layer
Make knowledge remember where it came from.
Source-grounded retrieval preserves lineage, confidence, and the origin of every approved response.
Private Generation Engine
Turn approved knowledge into useful experience.
Controlled multimodal generation remains protected behind the ECHO API boundary and customer tier controls.
Orchestration Layer
Make every protected layer move as one.
One enterprise interface coordinates governance, retrieval, generation, usage limits, and audit-ready output.
A CLEAR PATH TO OWNERSHIP
Every engagement has a defined commercial next step, from a paid architecture review to strategic exclusivity.
Discovery
Architecture, data-rights, and commercialization map.
SECURE DISCOVERY ↗Pilot
A proof-of-value deployment with measurable success criteria.
SECURE PILOT ↗Business
$25K setup plus a $100K annual proprietary license.
REQUEST BUSINESS →Enterprise
Private deployment, integrations, controls, and premium support.
REQUEST ENTERPRISE →Secure checkout is available for verified fixed-price offers. Payments are processed by Stripe; card details never touch this site. Purchase confirms payment and begins the project intake process.
Category or market exclusivity is available from $750K+ per year, subject to scope, term, and protected territory.
DISCUSS EXCLUSIVITY →
US PROVISIONAL 64/138,919 · PRIORITY AUGUST 22, 2026
VERITAS-BLACK X™ gives enterprises a deterministic control boundary between an AI decision and a consequential action. Patent pending under U.S. Provisional 64/138,919, the dual-cloud tested stack combines signed six-service evidence, recursive adversarial oversight, hardware-attested authority, Merkle verification, and fail-closed release control.
THE ENTERPRISE CASE · VERITAS-BLACK X™
The pilot inserts a separately governed release boundary between an AI recommendation and the action that can create financial, operational, legal, or public impact.
One model decision can cross into a consequential system without an independent, evidence-bound release gate.
Signed six-service evidence, adversarial oversight, Merkle verification, and fail-closed arbitration govern release.
Leadership receives defined acceptance criteria, resilience results, and an auditable pilot record.
Regulated AI workflows · financial decisions · critical operations · public-sector systems · enterprise agent actions
Workflow control map · threat model · bounded integration · acceptance tests · evidence package · executive readout
BPV-AU1 · BIO-ADAPTIVE EXPERIENCE PLATFORM
AURA converts supported physiological signals into bounded controls for wellness, research, and interactive experiences. It is positioned as non-diagnostic software: consent, signal quality, pause controls, and device-specific validation are part of the product—not fine print.
BPV-M01 · STREAM SECURITY BOUNDARY
M.A.P. IT™ is a standalone software boundary for high-value data and AI streams. It canonicalizes payloads, scores obfuscation and entropy, binds packet decisions to an HMAC-SHA3 integrity chain, and responds with bounded ALLOW, BLOCK, RATE-LIMITED, or TARPIT outcomes.
THE OPERATIONAL CASE · M.A.P. IT™
M.A.P. IT™ makes intake rules, risk decisions, and containment behavior explicit before a payload can move deeper into an application stack.
Encoded, abnormal, or high-volume traffic can consume resources and expose inconsistent edge behavior.
Canonicalization, entropy scoring, HMAC-linked integrity, and rate control produce explicit stream verdicts.
Non-blocking tarpitting and jittered circuit breaking create a fail-closed software response path.
AI prompt and output streams · API ingress · financial data flows · logistics telemetry · high-value application traffic
Endpoint integration · threat profile · test corpus · load and latency report · breaker and recovery evidence · deployment handoff
FLAGSHIP COMBINED OFFER · TWO PRODUCTS · ONE CONTROL ENVIRONMENT
M.A.P. IT™ enforces the stream boundary. VERITAS-BLACK X™ governs consequential release. Together they create a closed-loop enterprise sandbox around an AI workload—without merging either product's identity, evidence, or license.
Canonicalization, risk scoring, rate control, integrity chaining, tarpitting, and fail-closed stream verdicts.
Signed six-service evidence, adversarial oversight, Merkle verification, and deterministic release authority.
A defined control map, acceptance criteria, resilience results, and decision-ready evidence package.
Begin with one bounded workflow, then license additional streams, actions, business units, and environments.
FOUNDING SANDBOX PILOT
The engagement binds one high-value stream to one consequential release action under a written threat model, measurable acceptance criteria, and an executive go/no-go decision.
THE HOUSE OF GOVERNED INTELLIGENCE
Architect of GOD, GOD-MIND, ECHO STATIC, AURA, VERITAS, SPHINX, LOOM, FORGE, ECHO API, and M.A.P. IT™ retain separate identities, claims, offers, and license boundaries. Readiness is stated product by product.
Independent Product · Definition Gate
ENDURING PURPOSERemain a distinct product whose commercial claims come only from its own source, tests, and approved dossier.
WHAT EXISTSA standalone accessible vector master and cross-brand separation checks exist. No Architect of GOD core repository was supplied, so no software, performance, security, or production claim is made.
No paid pilot or license executes until scope, source, rights, tests, and acceptance criteria are documented.
Corporate AI · Enterprise Access Reference
ENDURING PURPOSEPlace corporate intelligence behind tenant-bound identity, enforceable entitlements, metered use, and immediate revocation.
WHAT EXISTSRelease 0.3.0 passed 29 Python checks, 10 frontend checks, and 3 independent brand-separation checks. This evidence covers access and licensing controls only; the GOD-MIND core AI was not supplied or tested.
Corporate SSO/OIDC belongs only to GOD-MIND. Live customer IdP, core tenant isolation, migration, load, recovery, and external security gates remain.
Sovereign Intelligence Suite
ENDURING PURPOSEGive institutions intelligence they can control, trace, and trust.
WHAT EXISTSThe governed stack architecture exists. Customer-specific integrations, production data, and SLA validation are completed inside the paid deployment.
Annual minimums, scoped integrations, and metered third-party usage.
Bio-Adaptive Experience Platform
ENDURING PURPOSETranslate supported physiological signals into bounded experience controls without presenting the result as diagnosis or treatment.
WHAT EXISTSVersion 0.3.0 passes 29 core tests covering signal normalization, consent, safety thresholds, session isolation, opt-in aggregation, and deterministic fallback behavior. Device and field validation remain pilot work.
Non-diagnostic positioning, explicit consent, device-specific validation, bounded adaptation, and written pause/stop criteria.
Hardware-Attested Recursive Oversight
ENDURING PURPOSECreate an evidence-bound release boundary for consequential AI actions while keeping the supervisory mechanism controlled.
WHAT EXISTSPatent Pending: U.S. Provisional Application Serial No. 64/138,919, priority August 22, 2026. Evidence includes RUN-20260825-072557-SUITE-FULL-005 (7/7 passed; 1.62 ms reported overhead), RUN-20260825-052211-RESILIENCE-003, and RUN-20260825-063558-CORE6-005 (6/6 services verified; Merkle root matched; final ALLOW), plus AWS and Google Cloud dual-stack testing.
Confidential mechanics, thresholds, keys, and exploit-sensitive details stay inside controlled review; public claims remain evidence-bounded.
Consent + Policy Control
ENDURING PURPOSEProtect permission, dignity, ownership, and sacred boundaries at machine speed.
WHAT EXISTSPolicy and consent gates are part of the ECHO architecture. Each production policy pack requires customer-approved rules and legal review.
Reusable policy packs, bounded evaluations, and no unmetered model calls.
Provenance + Memory
ENDURING PURPOSEPreserve the source, lineage, confidence, and right to revoke knowledge.
WHAT EXISTSThe retrieval and provenance design supports vector indexing and source lineage. Live quality depends on rights-cleared customer data.
Storage tiers, corpus limits, archival pricing, and customer-funded ingestion.
Governed Generation
ENDURING PURPOSECreate new experiences without breaking the rights attached to the source.
WHAT EXISTSThe generation boundary is designed for controlled multimodal providers. Output quality and cost are validated against the selected customer workload.
Prepaid credits, five-times variable-cost floor, and no unlimited generation.
Sovereign Control Plane
ENDURING PURPOSETurn separate safeguards into one observable, enforceable operating system.
WHAT EXISTSThe orchestration contract coordinates governance, retrieval, generation, and tier controls. Production throughput depends on deployed dependencies.
Throughput bands, idempotency, overages, and customer-funded connectors.
Standalone Stream Security Boundary
ENDURING PURPOSEProtect high-value application and AI streams with bounded intake, integrity-linked decisions, and fail-closed containment.
WHAT EXISTSThe standalone Python engine implements a 2,048-byte payload ceiling, 10-packet-per-second client control, a 10,000-client bounded LRU, Unicode and Base64 canonicalization, normalized Shannon entropy scoring, HMAC-SHA3-256 chaining, non-blocking tarpitting, and jittered circuit breaking.
One streaming boundary and threat profile per pilot, measured workload limits, annual minimums, and change orders.
Every proposal defines inclusions, exclusions, acceptance criteria, data handling, support boundaries, and the next commercial step before signature.
THE ATELIER · DISCIPLINES
Software. Engineering. Luxury. One House.
Proprietary software, paid pilots, monitoring, and enterprise licensing led by ECHO and M.A.P. IT™, with VERITAS maintained as a separate confidential control program.
OKAI ES600P deployment programs engineered for high-frequency use.
Exclusive products. Unconventional. Unattainable elsewhere.
FROM SOURCE CODE TO SCULPTURE — EVERY DETAIL IS AUTHORED.
For the few who demand the extraordinary.
BEGIN YOUR CONSULTATION→PRIVATE CLIENT SERVICES
DISCRETION. LUXURY. ACCESS.
“Exclusive access begins here.”— BE ALL PRIVATE CLIENTS
Prefer a more traditional approach?
LOCATION BY APPOINTMENT ONLY